 3 min read
 52
 Linkedin
 Threads
 Facebook
 X
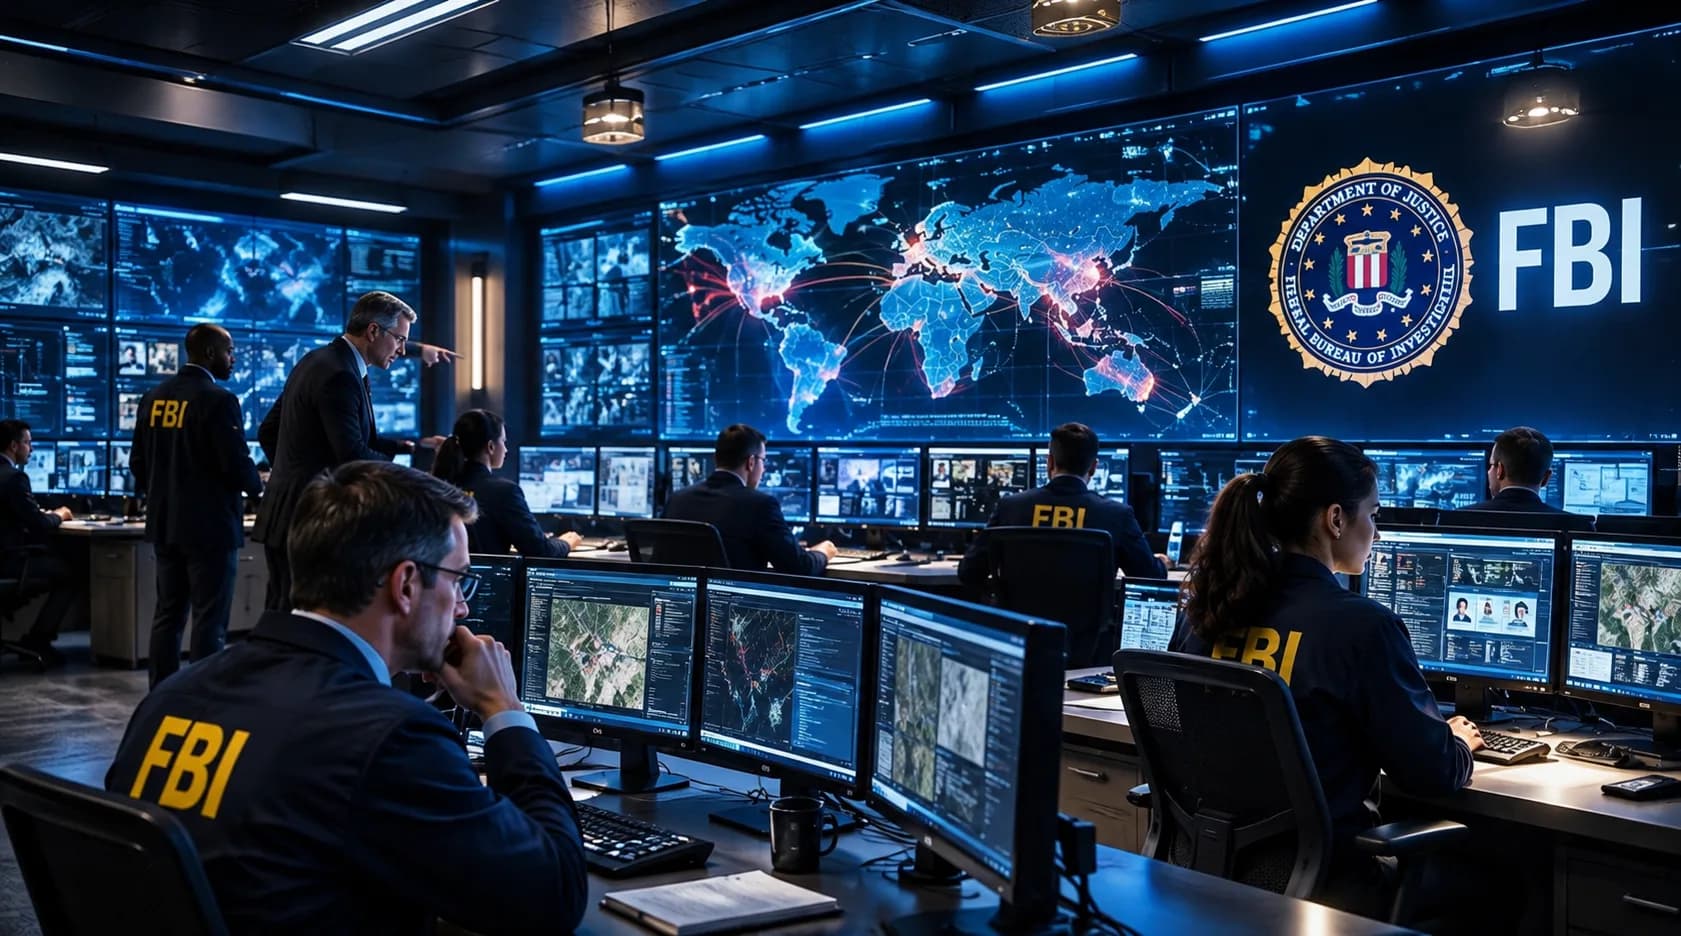
WASHINGTON, D.C. — November 18, 2026. The Federal Bureau of Investigation has issued a cybersecurity warning revealing how artificial intelligence is transforming cyberattacks, allowing criminals and state-aligned hackers to penetrate sensitive computer systems at unprecedented speeds.
The warning, published November 13 under FLASH-20261113-001, identifies ARTEX, an AI-powered penetration-testing framework that malicious actors have weaponized to automate sophisticated attacks against organizations worldwide.
According to the FBI, some intrusions have progressed from initial targeting to privileged system access in less than three hours.
What once required teams of experienced hackers can now be accelerated by autonomous AI agents operating with limited human supervision.
What Is ARTEX?
ARTEX was originally developed as an open-source cybersecurity testing framework.
Its purpose was to automate security assessments using large language models and specialized AI agents.
But investigators say cybercriminals have turned the technology into an offensive weapon.
ARTEX can automate reconnaissance, identify vulnerable applications, exploit weaknesses, escalate access privileges and extract sensitive information.
The FBI says attackers with relatively limited technical expertise can use the framework to conduct complex operations against multiple targets simultaneously.
Unlike traditional attacks requiring extensive manual intervention, AI agents can rapidly execute sequences of commands and adapt their activities.
FBI FLASH-20261113-001
Issued November 13, 2026 — Threat Overview of ARTEX Autonomous Penetration Testing Framework
Read the original FBI security advisory (PDF)
Banks, Defense Contractors and Government Systems Targeted
The FBI identifies attacks involving financial institutions, government organizations, technology companies, defense contractors, semiconductor manufacturers, energy providers, healthcare systems and telecommunications networks.
One campaign targeting South Korean financial institutions reportedly exposed personal information belonging to approximately 67,000 individuals.
Another attack involving ConnectWise Cloud Backup affected access pathways to more than 2,250 downstream Microsoft 365 customer environments.
Microsoft attributed that campaign to Storm-0940, a China-state-aligned threat actor.
The distinction matters: attempts to access thousands of customer environments do not mean every environment was successfully compromised.
Nevertheless, the campaign demonstrates how attackers can exploit trusted software relationships to reach multiple organizations.
More Than 1,600 ARTEX Consoles Exposed
The FBI reports that researchers identified more than 1,600 publicly exposed ARTEX console instances by early November.
The actual number of deployments could be considerably higher.
Although the original developer removed the framework's GitHub repository in October, copies continue circulating through archived repositories, modified versions and a commercial edition known as ARTEX PRO.
Removing the original software therefore did not eliminate the threat.
Could ARTEX Explain America's Recent Technology Outages?
The warning arrives amid a series of major disruptions affecting Microsoft services, airlines, banking systems, Apple and the National Security Agency.
The timing raises an understandable question: could AI-powered cyberattacks be responsible?
There is currently no verified evidence connecting ARTEX to those outages.
Several companies and government agencies have identified separate technical explanations, including software updates and infrastructure failures.
The FBI advisory concerns documented cyber intrusions beginning at least in August, not a confirmed coordinated attack behind November's outages.
The distinction is essential.
What Is the FBI Asking Organizations to Do?
The bureau recommends strengthening security around internet-facing applications, cloud administration systems, employee portals and third-party software connections.
Organizations should review access permissions, monitor unusual login attempts, investigate unexpected administrator privileges and watch for abnormal data transfers.
The FBI also encourages organizations to report suspected ARTEX-related activity through its Internet Crime Complaint Center.
The warning represents a significant development in cybersecurity.
Artificial intelligence is no longer simply helping companies improve productivity. It is also giving attackers new ways to accelerate operations that previously required substantial time and expertise.
The question is no longer whether criminals will use AI to attack critical systems. The FBI confirms they already are.
The challenge now is whether America's public and private infrastructure can adapt quickly enough to defend against attacks operating at machine speed.
Stay connected with FPTN for the real news. As is.